Bits from Bill

Technology thoughts leaking from the brain of "Bill Pytlovany"

Tuesday, August 19, 2008

Where did my Spyware come from?

Most folks will immediately blame another family member using their computer especially if they have teens in the house. In most case, it’s nobody’s fault if a machine is infected with some kind of spyware/malware/virus/badware, what ever you call it. So how the heck did your computer turn into such a mess.


Social Engineering
The number one method the bad guys have used for years is to just plain trick you. I’m sure you know not to reply to Email from the former ambassador to Nigeria but what if you get an alert message from Microsoft that says they found three viruses on your computer and you must download ie_update.exe?

Recently, we’ve seen updates of Internet Explorer and news videos that claim to be from CNN and MSNBC. They’re all meant to trick users into downloading badware. Convicted hacker Kevin Mitnick tells how in the old days he’d leave a floppy disk laying around public areas of a company with the label “Employee Salaries”.

I recently spoke at a conference for the National Network to End Domestic Violence. A common trick discussed was how perps would send an online greeting card that includes an apology but comes laced with a keylogger so the abuser can spy on all future computer activity.

The use of social engineering to try and take over your computer will continue to be number one method and will certainly improve and get more sophisticated. You’re sure to see a lot of this type before holidays and anytime there’s a huge world wide event.


Software Vulnerability
You probably all know about those regular software updates from Microsoft, Apple, Adobe and others. I’m not a big fan of “auto”updates but downloading security patches isn’t a bad idea. I usually wait until they’ve been released for a week or so and have been tested by the rest of the world. After that I do recommend having your system software updated with any patches available.

A software vulnerability can install a program on your system without downloading or clicking on any suspicious links. Anytime you’re connected to the internet your computer is probed to see if it’s visible and if any vulnerabilities exist. If the right vulnerability exists when your system is polled it can become the property of the first bad guy to find you.

I experienced one years ago when MSBlaster suddenly appeared on my computer. Luckily, WinPatrol was on patrol and I was immediately asked if this was something I had installed. I didn’t know what MSBlaster was so I removed it. This was a brand new threat so none of the anti-spyware/virus programs had any information about msblaster in their signature files.


Music and Porn Sharing
Seriously, I don’t have a lot of first hand research on this particular segment but I do what I have to in the interest of knowledge.

While this may get much of the blame in many households its not as prevalent as it used to be. That’s not to say that surfing for music and porn isn’t a malware mine field, it’s just that infections are a little more obvious. You know you’re in trouble when the only way you can close the browser Window is to completely shut down the browser or reboot your machine.


You don’t really have Spyware
One of the main reasons people purchase new computers is because their old computer is slow due spyware. In many cases when I’ve been asked to clean up spyware I find the system is basically clean. Usually, the computer is old, and has had so many programs installed and uninstalled over the years that the version of Windows on their computer is just plain tired out. How’s that for a technical quote?


Windows is a collection of various programs and libraries. Over many years of installing new programs different versions of Window components may be installed. This can become a big hodgepodge of files and old drivers so that no two versions of Windows are the same. We used to joke that Windows 95 wasn’t the year it was released. It meant every 95 days you should reformat your machine and reinstall Windows from scratch.


My best advice for these machines would be clean up auto start programs, add memory, clear up as much disk space as possible, and especially clean up any temp files including the Internet Explorer cache. Others swear by defragging your disk or using registry cleaners but I’m not a big fan.


Additional References:

Windows Versions are like Snowflakes

AutoUpdates are Evil

Do I Need a Registry Cleaner?

Your PC is NOT old

Labels: , , ,

Share on Facebook


Saturday, February 02, 2008

How Do We Stop Spyware?

A number of folks who have been on the forefront of battling spyware and adware met last week in Washington D.C. I’ve been to a number of AntiSpyware conferences over the years and they seem to get better all the time.


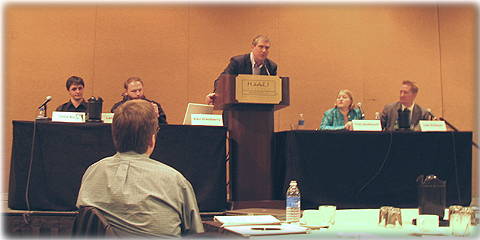
Panel called CSI Spyware: Can Investigators Stay Ahead of the Bad Guys.
CSI Spyware: Can Investigators Stay Ahead of the Bad Guys?

From left to right

Seated up front is longtime supporter of the MyWay searchbar, Kirk Lawrence, IAC Search & Media.

It’s hard quantify what kind of difference these meetings make. In a way it’s like a pep rally that gets many of us excited and motivated to continue our efforts. It’s also excellent to share stories and methodology. While many participants are essentially competitors the cooperation is unlike other industries.

Chris Boyd has posted some photos from the conference as well as some fun tourist travels on Flickr. There’s even proof that I sometimes wear a suit and tie. It’s interesting to view our country through new eyes. Click the photos below for more.

Photos by Chris Boyd during his recent adventures in the colonies.
NYC as viewed by a visitor from across the pond.


Labels: , , , ,

Share on Facebook


Thursday, January 03, 2008

Anti-Spyware Coalition Still Alive

Later this month, I will be getting together in our nations capital with a number of our friends to discuss that state of spyware. The Anti-Spyware Coalition is holding the event which will consist of various moderated panels.

  • User Behavior and Spyware

  • Anti-Spyware Liability

  • Is Adware Dead?

  • CSI Spyware: Can Investigators Stay Ahead of the Bad Guys?

  • Education: What Works and What Doesn’t?

The event is open to the public but a $250 admission fee is required unless you’re connected to the government or educational institution. For more information go to http://antispywarecoalition.org/events/jan2008.php


I’ve attended a number of events like this in the past and they’ve all been extremely successful. While the panels can be informative the behind the scenes dinners and informal meetings really make a difference. Every time I’ve gotten together with other good guys it has resulted in an avalanche of information sharing. It also motivates me to get off my butt and continue to make a difference. I’ve been trying to come up with the next big change to WinPatrol and I suspect this meeting will spark an idea.

I’ve posted photos and made mention here of half the planned panel members. There are a few I haven’t met in person yet so I’m really looking forward to this months event. You can click the link above to get a list of who will be participating.


Other references:

CSI Spyware: Better than the TV Show (PaperGhost)
Antispyware Coalition: The History and Future of Spyware (Donna)
Save the date: Anti-Spyware Coalition public workshop (stopBADware.org)

Labels: , , ,

Share on Facebook


Friday, November 30, 2007

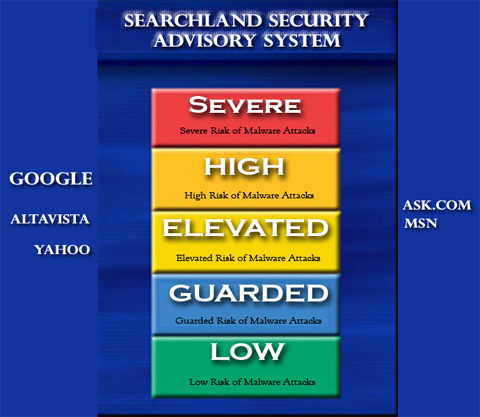
Searchland Security Advisory High

If you haven’t gotten around to updating your anti-virus software and/or installed the newest Windows update patches the time is now! In the last few weeks our users have reported 3 times the normal number of malware attempts.

One new approach is to bomb search engines with malware sites. Google and others have been cleaning up their results as quickly as possible but it’s an ongoing battle.

HEADS UP: More Google poising on the way? SunbeltBLOG


Malware Advisory


If you think the search engines are in the business of filtering out the bad guys you would be wrong. Even some paid advertising was recently found to send folks to malware sites. They do their best to keep you safe but that’s not really their responsibility.

The bottom line is you need to take steps to stay safe. Here are just a few timely tips.

  • Update Windows
    One of the most common entries into your system is a well known vulnerability you’ll see referred to the IFRAME exploit. Microsoft has corrected this problem and as long as you’ve installed all the Windows Update patches you’re better off.

  • Don’t download that CODEC
    A popular trick to get users to download files is to make you think it’s required. It doesn’t have to be a video of a naked Brittney. It could be a video of a cute kitty but if it says, you must install this codec before viewing the video, STOP.

  • Your computer is not a “potential Spyware operation”.
    Don’t fall for a pop up that says your computer is infected. Even if this is true any web page that detects this without you asking is a scam. You’ll end up with is Rogue Anti-Spyware software which will exhort a payment from you before giving you control of your own computer. If you want security software go with a known company.

  • Disconnect your computer at night. (New)
    Turning off your computer at night has long been debated within the computer industry and I won’t get into it now. I will advise at the least, disconnect your computer from the Internet when not in use. Even if you think your computer is clean you could may infected and your computer could act as a “bot”. You’re also at risk to be infected by some vulnerability like MSBlaster that hasn’t been made public yet. If everyone got in the habit of turning off the internet when not in use it couldn’t hurt.

Labels: , , , ,

Share on Facebook


Wednesday, October 24, 2007

Direct Revenue Wasn't a Better Internet

I’ve had a lot to celebrate this month. I have a new grand niece, Ella Grace Pytlovany born Oct 11th. On October 15th our nephew John returned from his 2nd long tour in Iraq. Today, I received the good news that Direct Revenue LLC and Best Offers Networks have ceased operations.


The folks behind “A Better Internet” and MyPCTuneUp.com were well known for invading and taking over PC’s without a users knowledge or permission. In April 2006, New York State sued Direct Revenue and I reported on the results here in my post, “Death Threats for A Better Internet “. These guys knew all the tricks and showed no mercy yet, they thought it was a legitimate business model.


Last years lawsuit included relief and penalties from, the company's founders and chief officers Joshua Abram, Alan Murray, Daniel Kaufman, and Rodney Hook. It will be interesting if these names appear in any new companies or if they’ve learned anything from past consumer responses to their dastardly deeds.


Thanks to researcher Ben Edelman, Assistant Attorney General Justin Brookman and all the others who spent time and resources to expose these guys.

Labels: , , ,

Share on Facebook