Bits from Bill

Technology thoughts leaking from the brain of "Bill Pytlovany"

Monday, March 17, 2014

Safe Updates & Discounts For Windows XP

There are a variety of services that help keep your important software updated. We've added a  "Check for Safe Updates" button  to integrate a new version checking feature directly into WinPatrol. It won’t be the most powerful but in the WinPatrol spirit our goal is to make sure updates are safe and folks are educated to all possible risks.
safeversionbutton


Previously this button checked for new versions of WinPatrol but it has been expanded to include version checks for popular software packages. When you click this button we'll compare your version against the newest safe version available. If updating is recommended you'll see a safe link that goes to the official download page for the software.

This is critical because bogus sites are showing up on the top results page with Google, Bing and other search engines. It's easy to find yourself on web page that tries to trick you into downloading software wrapped with a setup program that installs additional unwanted software.

Even a legitimate company like Oracle has partnered with toolbar and anti-virus companies. The revenue they get when anyone installs the parasitic software is significant. Considering the installed base of Java users and now often they need security updates it’s a very lucrative market. The WinPatrol PLUS Safe Update Engine will also warn you about these threats and show you sample screen shots of what you might expect.

javaask
Every time a new version of Java is available Oracle will try to push other software unrelated to Java. In some cases they’ll receive over a dollar for each customer lead.

Restore Deleted Files

Our second big feature came after feedback from radio host and America’s Digital Goddess, Kim Komando. In a recent article, Kim recommended WinPatrol but cautioned her readers about the dangers of deleting files that may be required. WinPatrol has always provided a History button that allows you to Restore any Startup Programs but she had a point when it comes to the removal of hidden files.

The files will now quarantined in a WinPatrol vault. We will also include a command line scripts that can be used to restore any files that had been hidden. The command-line scripts are created for a worse-case scenario when someone deletes a file that is required for Windows to run. The script or .bat file can be run in safe mode or a command-line mode.

PLUS Discount for Windows XP

The new Safe Update Engine will also detect which version of Windows you're running. If appropriate we will advise you to any potential problems. For instance, if someone is still using Windows XP we will offer timely protection tips. It’s clear not everyone can or will be upgrading immediately. Some businesses have software or hardware that still requires Windows XP.  Unfortunately, an XP machine could be infiltrated and turned into a "bot" that could be used to send SPAM or deploy viruses.

If our Safe Update Engine detects you're using Windows XP you'll see a link to a special Windows XP purchase page. The name of this page will routinely change but it will have a PayPal button that allows you to upgrade to WinPatrol PLUS for only $2.00 USD. If you can’t afford a Windows upgrade we’ll make sure WinPatrol PLUS is affordable.

safeupdatexp

This is section of the results provided by the WinPatrol PLUS Safe Update Engine. In this example, the special offer is provided when the Safe Update feature detects Windows XP is running.

Labels: , , , , , , , , , , ,

Share on Facebook


Friday, July 31, 2009

Security Vulnerabilities near Apocalyptic Proportions

We’ve had a heck of a week in the security world. I really don’t know where to begin. Most people think of the Apocalypse as the end of the world but the origin of the term is the “disclosure to certain privileged persons of something hidden from the majority of humankind”. That’s what happen this week. Those who were paying attention were informed about a number of security flaws that hopefully have been corrected. If you haven’t taken advantage of these updates you should.

The first came from Microsoft with what’s called an “out of band” security update. If you think it sounds serious, you’re correct. If you don’t have automatic updates on your Windows machine, it’s time to run the Windows update program.

Microsoft Security Advisory 973882
Microsoft Security Bulletins MS09-034 and MS09-035


Also on Tuesday the folks at Mozilla admitted there’s a vulnerability in Firefox where “The URL in the address bar can be spoofed when a new window or tab is opened by a malicious web page.” This could result in a phishing attack and not necessarily a huge issue. Mozilla has found and fixed this issue which will be rolled out in the next release.


On Thursday Adobe announced “Security updates available for Adobe Flash Player.“ This vulnerability could allow an attacker to take control of your machine if you’re running Windows, Mac OS and even Linux. More info at http://www.adobe.com/support/security/bulletins/apsb09-10.html. Adobe also recognizes that their Shockwave Player is affected by the recent Microsoft advisory so they recommend upgrading to the newest Shockwave Player at http://www.adobe.com/support/security/bulletins/apsb09-11.html


The fun really began at the BlackHat Security conference when three researchers acknowledged they provided Apple with details on how they could hack into and take control of someone's iPhone. They gave Apple two weeks to fix the problem before making the information public. Apple announced today they will be updating users the next time they plug their iPhones into their computers. Unfortunately, one of the vulnerabilities discovered affects more than just the iPhone. A large number of phones which accept SMS messaging may be at risk.


Before you want to go running for the hills I’ll share one last bit of news. Remember all the talk earlier this year about the Conficker virus? Well, stay-tuned this month to hear about the financial trojan called Clampi. This one may also get more attention then you think it deserves but there’s no doubt what the purpose of Clampi is. It’s all about the money.

“Clampi banking trojan misdirects business wire transfers.”


Have a great weekend!


Labels: , , ,

Share on Facebook


Monday, February 11, 2008

Time to Update Adobe Reader

Regular readers know that I don’t always encourage folks to download updates immediately after they’re released. For instance, tomorrow Microsoft will be releasing a new update that fixes a number of issues. Included are 7 critical fixes and 5 important fixes. I usually recommend waiting 7–10 days just to make sure there aren’t unique problems caused by these updates.

Past articles:

I do have an exception this week. Adobe has released a fix for their popular Adobe Reader which is used to render PDF files. In the past, Adobe Reader was a program you’d download as needed but PDF files are now so popular it’s extremely likely the Adobe Reader has already been installed on your system.

A number of malicious PDF files have been seen in the wild and we’ve had reports of infection attempts using a vulnerability in Adobe Reader. You can update your system by downloading the new Adobe Reader at http://www.adobe.com/products/acrobat/readstep2.html


You probably want to uncheck the Photoshop Starter Album

In the grand tradition of companies trying to shove their other products down our throat you’ll see a pre-checked box encouraging you to download the 50 MB Photoshop Album Starter Edition. While this may not be a bad package, I recommend you uncheck the box and concentrate on just updating that Adobe Reader. That way if you do have some kind of problem you’ll know which application introduced the change.


Labels: ,

Share on Facebook


Sunday, January 27, 2008

Online Activation is the Future

I’ve always been fairly open minded when it comes to software piracy. I’ve always known that a number of people were using illegal PLUS codes. Until recently I didn’t realize how many! I figured the folks using generated code were probably not going to support WinPatrol anyway so it’s not like I was losing money. However, it really isn’t fair to those friends of Scotty who have shown their support over the years.

After doing some research, I decided to take step one in clamping down on illegal codes. I want to make sure all legitimate supporters had the quickest possible access to the PLUS database. They deserve the best. Online activation seems to be making a difference and has already shown me just how many people have been naughty.

Over the last two days over 4000 activations have been attempted using codes which weren’t provided by BillP Studios. Most attempts came from specific locations in the world. Some repeated attempts are coming from a few folks determined to create new keygen schemes.

Message when illegal PLUS codes are entered

In some cases we will have problems with our long time PLUS members who may have typed a number one where the letter L should go. I’m standing by the computer and responding to Emails quickly to get folks back using PLUS as quickly as possible.


WinPatrol Update

In other news, those of you who were quick to download our newest version may want to stop by again. I did find a bug that, depending on your processor type, may delay new startup alerts. It’s amazing and embarrassing how much changing a compiler setting can affect software. WinPatrol 14.0.2007.1 is available at http://www.winpatrol.com/download.html.

Labels: , , ,

Share on Facebook


Friday, November 30, 2007

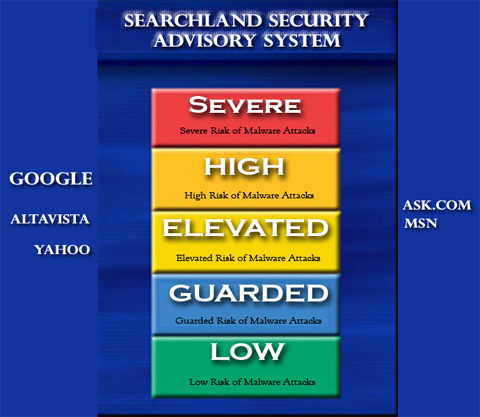
Searchland Security Advisory High

If you haven’t gotten around to updating your anti-virus software and/or installed the newest Windows update patches the time is now! In the last few weeks our users have reported 3 times the normal number of malware attempts.

One new approach is to bomb search engines with malware sites. Google and others have been cleaning up their results as quickly as possible but it’s an ongoing battle.

HEADS UP: More Google poising on the way? SunbeltBLOG


Malware Advisory


If you think the search engines are in the business of filtering out the bad guys you would be wrong. Even some paid advertising was recently found to send folks to malware sites. They do their best to keep you safe but that’s not really their responsibility.

The bottom line is you need to take steps to stay safe. Here are just a few timely tips.

  • Update Windows
    One of the most common entries into your system is a well known vulnerability you’ll see referred to the IFRAME exploit. Microsoft has corrected this problem and as long as you’ve installed all the Windows Update patches you’re better off.

  • Don’t download that CODEC
    A popular trick to get users to download files is to make you think it’s required. It doesn’t have to be a video of a naked Brittney. It could be a video of a cute kitty but if it says, you must install this codec before viewing the video, STOP.

  • Your computer is not a “potential Spyware operation”.
    Don’t fall for a pop up that says your computer is infected. Even if this is true any web page that detects this without you asking is a scam. You’ll end up with is Rogue Anti-Spyware software which will exhort a payment from you before giving you control of your own computer. If you want security software go with a known company.

  • Disconnect your computer at night. (New)
    Turning off your computer at night has long been debated within the computer industry and I won’t get into it now. I will advise at the least, disconnect your computer from the Internet when not in use. Even if you think your computer is clean you could may infected and your computer could act as a “bot”. You’re also at risk to be infected by some vulnerability like MSBlaster that hasn’t been made public yet. If everyone got in the habit of turning off the internet when not in use it couldn’t hurt.

Labels: , , , ,

Share on Facebook