Bits from Bill

Technology thoughts leaking from the brain of "Bill Pytlovany"

Tuesday, April 29, 2014

Computer Security Will Never Be the Same

This has been a remarkable month and the impact on how I view computer security will never be the same. The last time anything like this occurred was in the 90’s when I was infected with a complex worm looking to steal AOL passwords. When customer support told me to format my hard drive it encouraged me to create WinPatrol. The concept used in WinPatrol had never been done before but since my programming skills were busy on other projects it remained just a side project.

aprilI started April 2014 making it clear what Microsoft’s lack of support for Windows XP would really mean. By the end of the month the worse case prediction appears to be coming true. Microsoft received details of an active zero-Day vulnerability from security platform developer,
FireEye.  Not only does this threat affect nearly all versions of Internet Explorer and Windows,  attacks using this vulnerability are currently being reported. 

The software  already “in the wild” uses a Flash(.swf) file to call JavaScript in Internet Explorer eventually accessing protected memory that had been randomized as a form of protection. The entry method has been a known flaw since last October but until now wasn’t found to trigger this kind of attack. Microsoft has posted a new security advisory at https://technet.microsoft.com/en-US/library/security/2963983. The Microsoft Security Response Center has been working through the weekend  testing a solution they hope to release soon.  Even though the flaw is in Internet Explorer if you’re using Windows XP you won’t receive an update. No matter how much you’re tempted to view a video you hear about on Facebook, Twitter or in your Email, don’t do it.

tvbleed

The other major concern in April was called Heartbleed.  While the media coverage was over the top, few really understood what this software failure meant.  You may have heard that 66% of the worlds web servers were affected. In fact, less than 7% were actually running a version of the program OpenSSL that allowed access to 64kb chucks of data belonging to others.  Even with this seemingly low number, Heartbleed opens up a couple of troubling issues. Problem #1: Data exposed by this flaw was raw and unencrypted. It was available to anyone no matter how secure you made your computer or how sophisticated the attack. The attacker didn’t need to know you to access your data.  Problem #2: This event demonstrated how defenseless we all are any time we use the Internet. This was the result of a programmer and reviewers missing a simple error. I can only imagine how much of the Internet uses software with existing backdoors created by design.

This year I’ve done a lot to make WinPatrol easier and useful to a wider audience. Given these serious threats my motivation hasn’t diminished.fontalert The basic concept of WinPatrol detecting changes continues to be a model that make sense. While some attacks may require the PLUS version we have one advantage. Ironically, WinPatrol isn’t always taken seriously so it continues to notify users while many popular Anti-Virus programs are disabled.

.


UPDATE 5/2/2014
Microsoft has released a security update on May 1st.  This update will repair the failure found in Microsoft Internet Explorer.
Security Garden: Out of Band Security Update for IE Zero-Day Vulnerability
The patch is available as a Windows Auto Update.   Microsoft surprised many by making this available on machines running Windows XP.
WinBeta: I’m sorry Windows XP users, but Microsoft shouldn’t have patched your OS

Labels: , , , , , , , , , , ,

Share on Facebook


Tuesday, December 16, 2008

Zero Day Vulnarability for Internet Explorer

Over the years most of you have been inundated with buzz words like virus, spyware, worm, trojan, rootkit and over the last year Zero Day has been popular. The zero-day term refers to an attack or virus which is previously unknown so no patch or virus defination is available to catch it on day zero.  It won’t be caught by your antivirus scanner because they don’t know about it yet. 

A Zero Day “Vulnerability” is the worst. This attack uses a flaw in a program such as the browser that allows code to execute with no warning to a user. You don’t have to be tricked into downloading anything. All you need to do is to visit a web site or in some cases just be connected to the internet. The only protection will be programs like WinPatrol that monitor for changes to your system.

This week Microsoft has released an advisory to protect users until a patch is available.  Click “Vulnerability in Internet Explorer Could Allow Remote Code Execution”. Microsoft advises some pretty serious work arounds including.

  • Set Internet and Local intranet security zone settings to "High" to prompt before running ActiveX Controls and Active Scripting in these zones
  • Configure Internet Explorer to prompt before running Active Scripting or to disable Active Scripting in the Internet and Local intranet security zone
  • Disable XML Island functionality
  • Restrict Internet Explorer from using OLEDB32.dll with an Integrity Level ACL
  • Disable Row Position functionality of OLEDB32.dll
  • Unregister OLEDB32.DLL
  • Use ACL to disable OLEDB32.DLL
  • Enable DEP for Internet Explorer 7 on Windows Vista and on Windows Server 2008
  • Disable Data Binding support in Internet Explorer 8 Beta 2


These are pretty drastic actions but this threat should be taken seriously. Most experts are recommending folks stop using Internet Explorer completely until Microsoft has a patch available. I’m among those experts who also recommends finding a new browser for a while. Personally, I’ve become a fan of Google Chrome which is now out of beta and has an official version 1.

Alternate Browsers in order of my preference:

Download FireFox

Download Google Chrome

Download Opera 

Download Apple Safari (You may have already be tricked into installing this along with iTunes)

Update: Microsoft has released an emergency patch to fix this serious vulnerability.  http://www.microsoft.com/technet/security/bulletin/ms08-078.mspx

Labels: , ,

Share on Facebook


Monday, August 13, 2007

FlashPix ActiveX ZeroDay Fix

My good buddy Alex over at Sunbelt Software alerted me to a new Zero Day vulnerability that has been announced by US-Cert(United States Computer Emergency Readiness Team). The bug was discovered and demonstrated yesterday by Krystian Kloskowski.


This is the kind of infection that can occur just by going to the wrong web page or reading an HTML document. You don’t have to download or agree to anything for this kind of threat to attack your computer.


The flaw was found in a file “DXTLIPI.DLL” which may or may not exist on your computer. This file is the container of an ActiveX control from Live Picture Corporation known as “FlashPix”.


The only available solution requires a change in the registry so the current version of this ActiveX will not be executed by Internet Explorer.


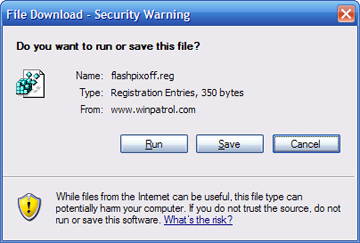
For those who aren’t comfortable using Regedit, I have created a registry script which will make the change for you. Just run the following to protect your computer. You can also save it to your computer and run it after download.

http://www.winpatrol.com/support/flashpixoff.reg

You'll see the following dialog

This script will set the kill bit for this ActiveX definition. If you’re using Netscape, it won’t run the script, it will just display the text contained in the script. Of course, if you’re using Netscape, you don’t have to worry about it anyway. Wink Wink


Labels: , , ,

Share on Facebook